Insider threats are among the most difficult attacks to detect. Compromised credentials, malicious insiders, privileged accounts and, increasingly, autonomous AI agents and other non-human identities can all introduce risk from within trusted environments. Traditional security tools rely on static rules, known patterns and the assumption that trusted identities behave as expected, so subtle shifts in behavior go unnoticed. Organizations remain exposed to data theft, fraud and operational disruption originating from within their own networks.
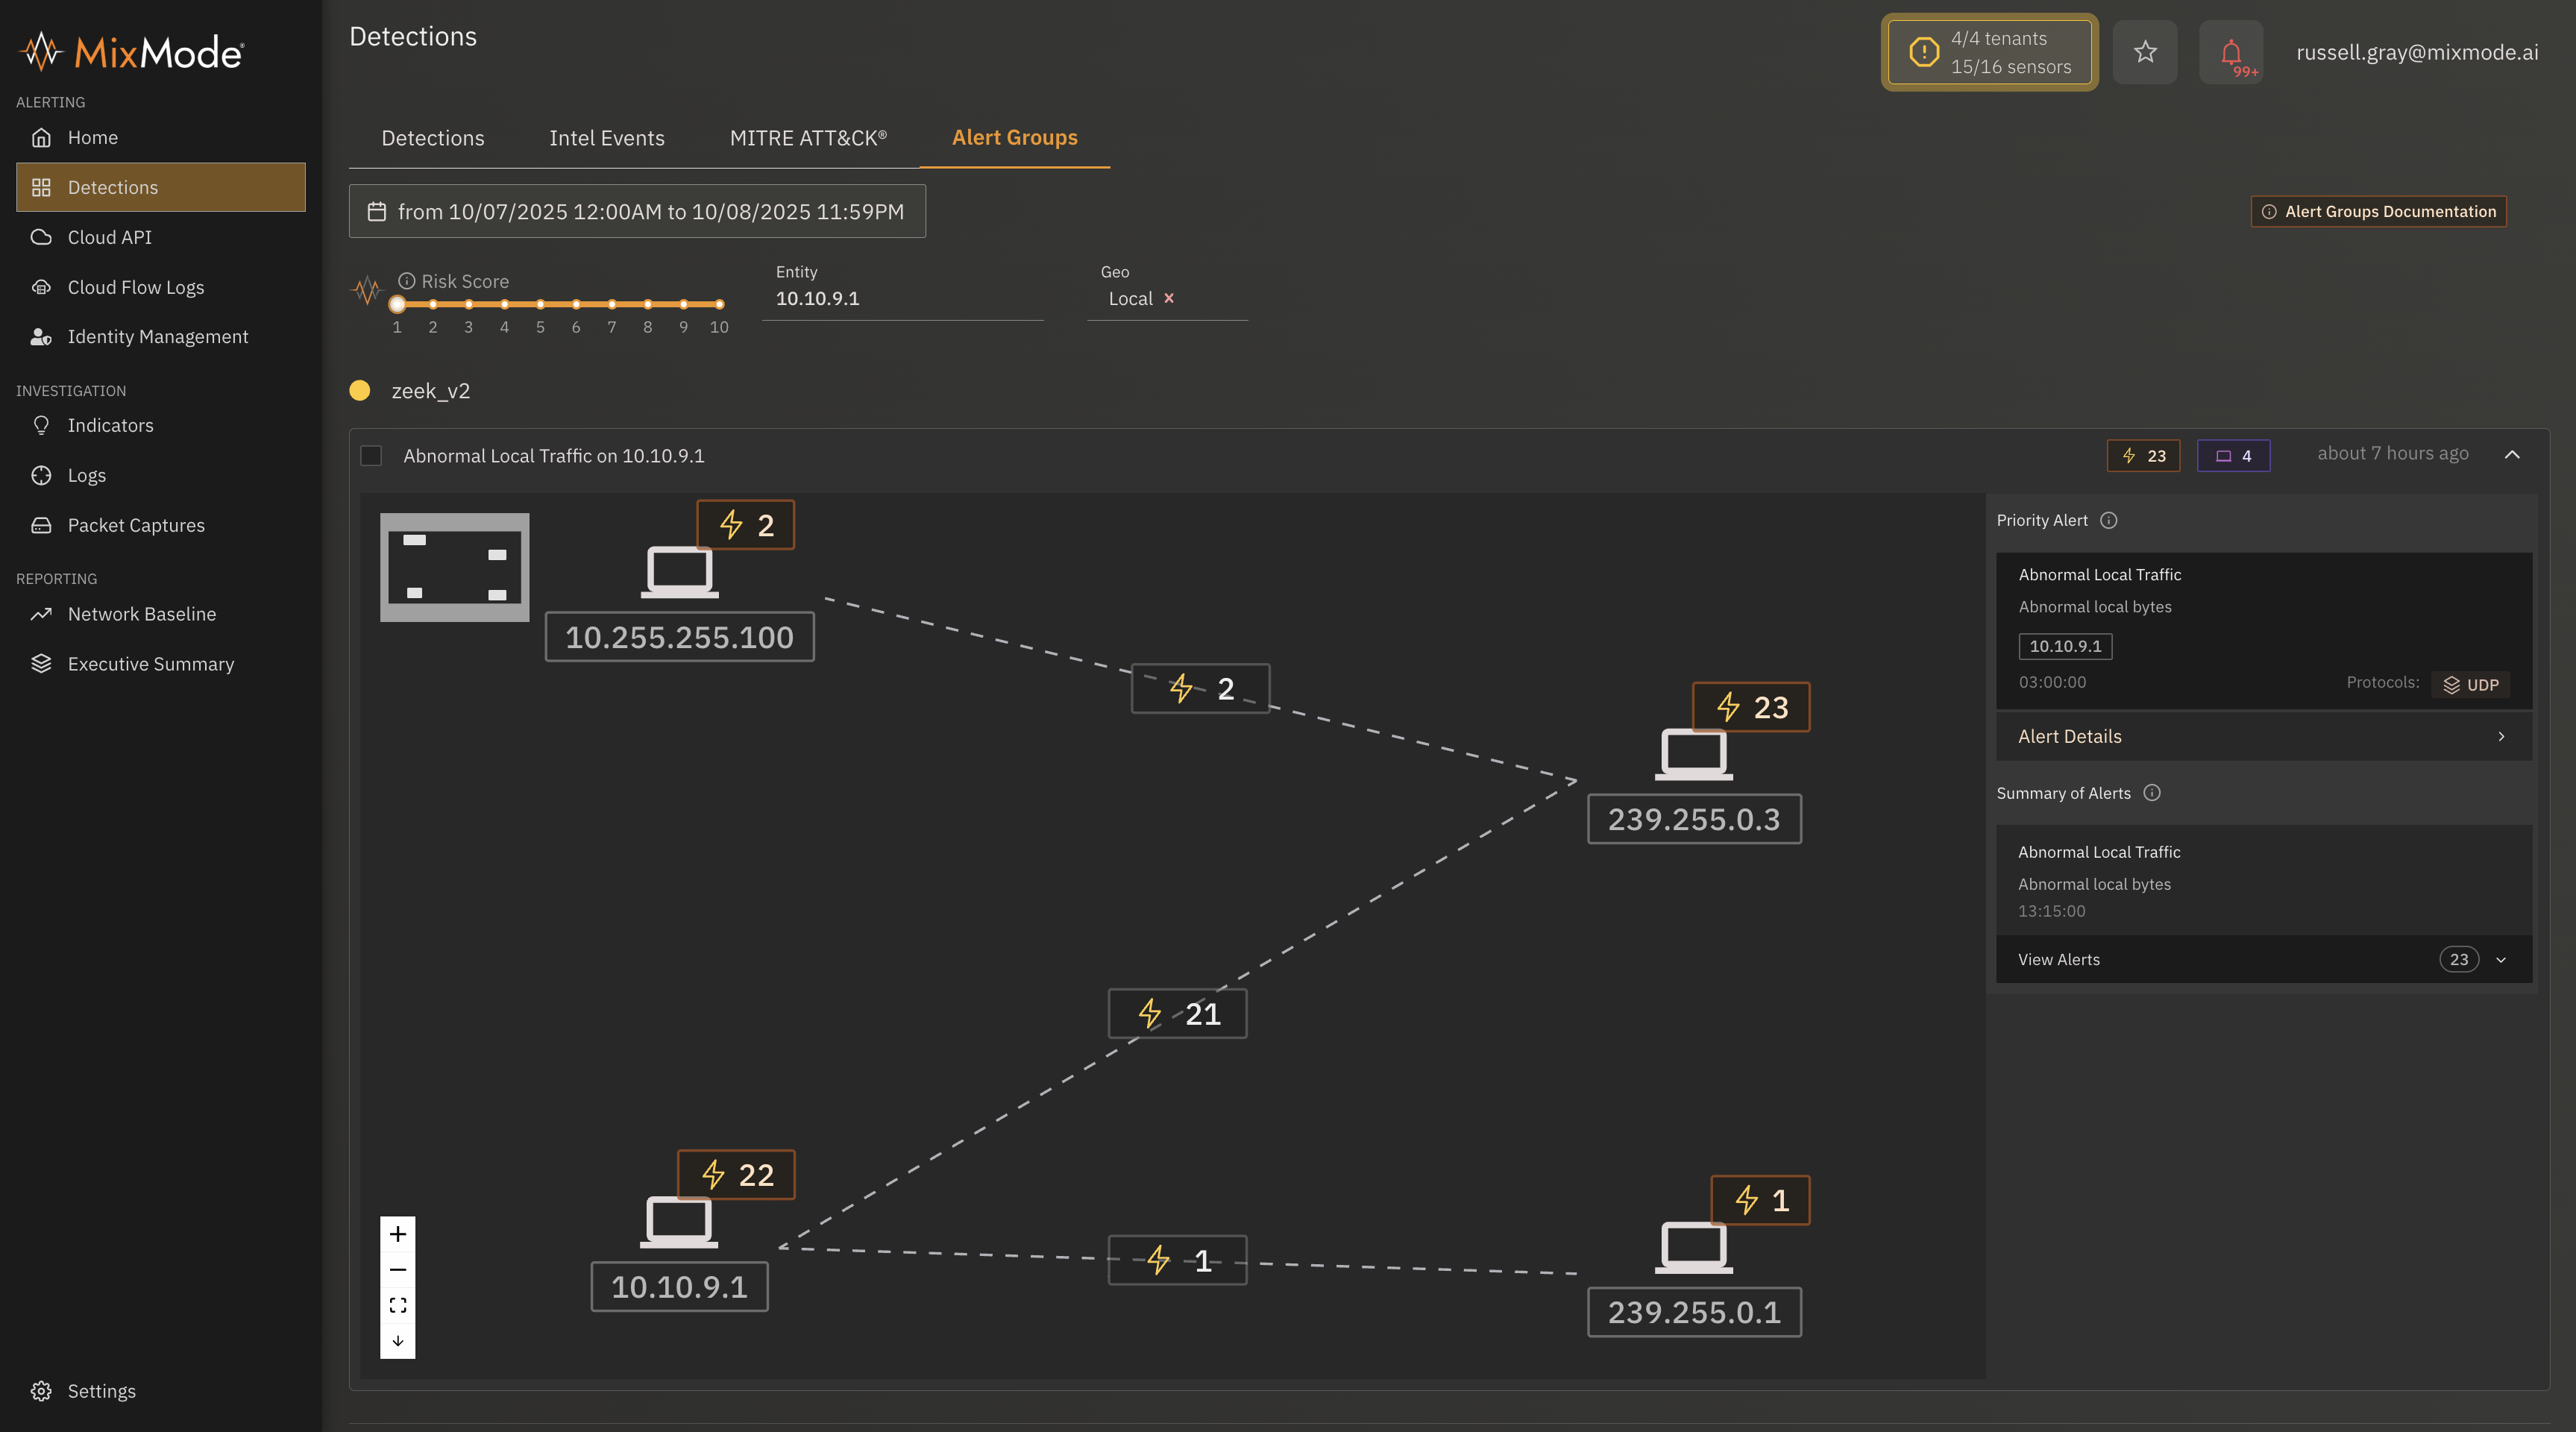
MixMode’s self-supervised AI continuously analyzes behavioral patterns across users, accounts, AI agents and systems to identify unexpected activity in real time. By autonomously learning what is expected in each environment, MixMode detects deviations that may signal insider threats, unauthorized access or compromised systems, without depending on signatures or preconfigured rules. Because it focuses on behavior rather than simply trusting identities or permissions, MixMode helps security teams uncover suspicious activity that traditional security controls may overlook, then investigate and respond quickly.
Click the button below to download the Platform Data Sheet.